996 Zyxel Switches Looted in 48 Countries; Patch Due Sept. 24
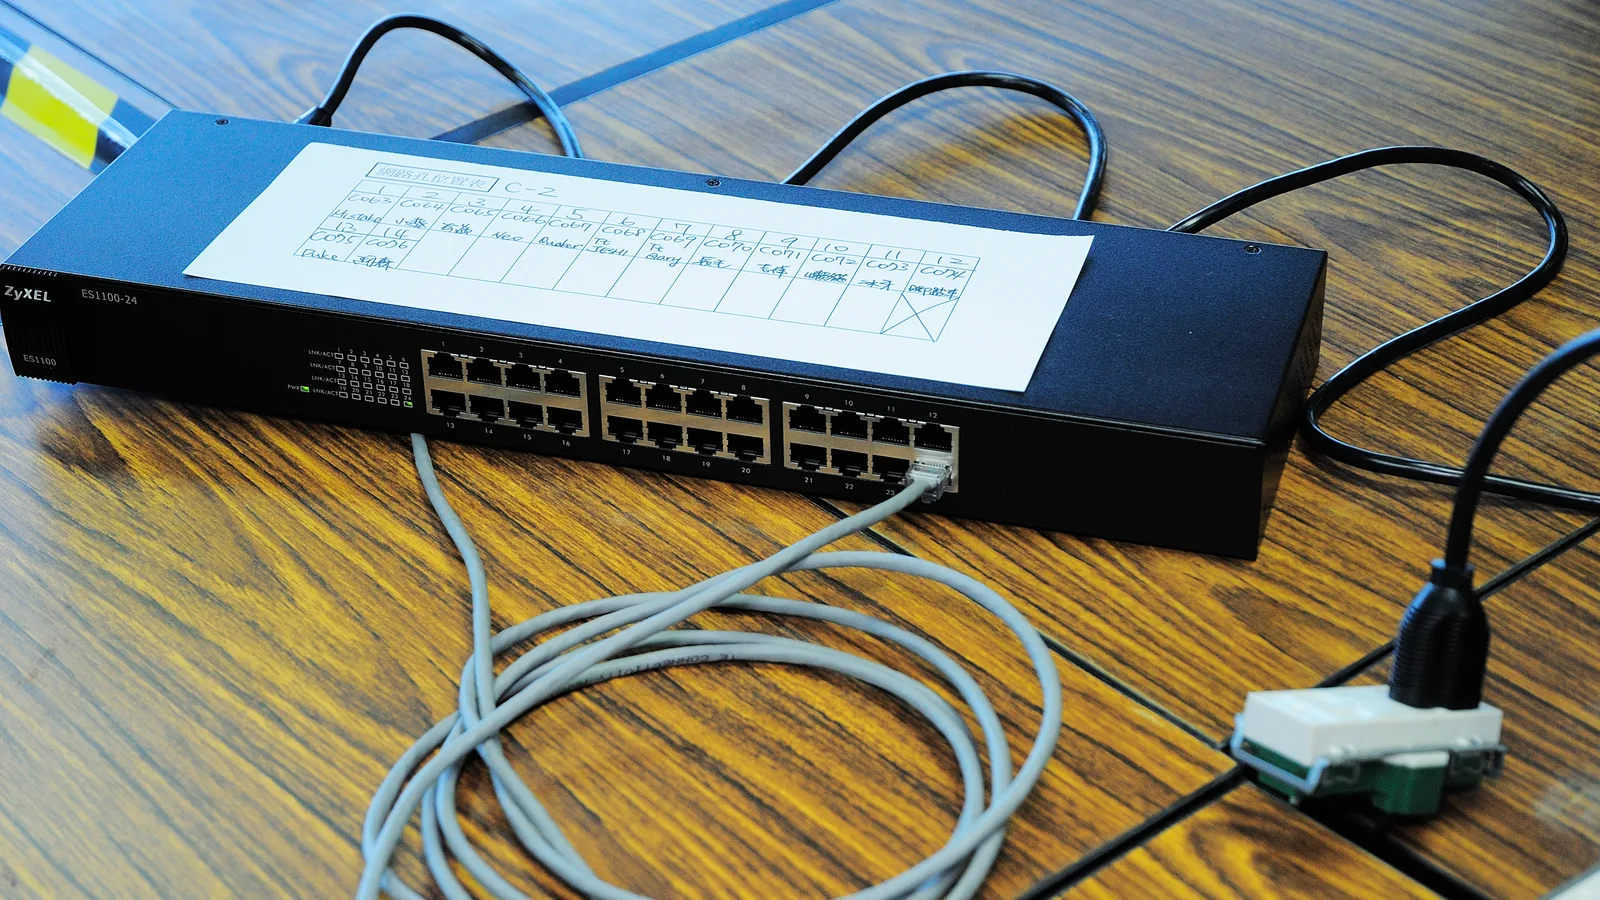
Nearly a thousand internet-facing Zyxel network switches have been quietly stripped of their credentials and configuration files, and the US government's patch deadline for the flaw behind it falls on 24 September.
The bug is CVE-2026-7273, a stack-based buffer overflow in the CGI program of Zyxel's GS1900 line of smart managed switches — the inexpensive 8- to 48-port boxes that sit in small offices, school closets and branch racks. Zyxel scores it 8.8 out of 10 on the CVSS scale, according to the National Vulnerability Database: a LAN-based attacker with no credentials at all can send a crafted HTTP request and run operating-system commands on the device.
Security firm GreyNoise says a suspected Chinese-speaking threat actor has been weaponising it since on or about 17 August 2026, and had successfully exploited and exfiltrated data from 996 Zyxel switches across 48 countries by the time it published on 22 September. The haul included device configuration files, network information and hashed root-level credentials — material that maps a victim's internal network and can be cracked offline. The exploit arrived as a Python script heavily obfuscated with the commercial tool PyArmor, which then used TFTP to fetch and run a custom collector script, The Hacker News reported. Italy, the United States, Taiwan, France and South Korea are among the countries hit. Researchers describe a possible overlap with a cluster tracked as Red Heron, but stop short of firm attribution.
Why now: CISA added the flaw to its Known Exploited Vulnerabilities catalog on 21 September 2026 and set 24 September as the remediation due date. That deadline is binding on US federal civilian executive branch agencies under Binding Operational Directive 26-04; every other organisation is encouraged, not ordered, to act. GreyNoise told BleepingComputer that “As of 17 September 2026, this is the first publicly documented case of exploitation in the wild of this vulnerability.”
The uncomfortable detail is the calendar. Zyxel published its advisory and fixed firmware on 16 June 2026 — two months before the campaign started — crediting Lei Gu, Jun Cao, Zhiqing Rui, Jingzheng Wu and Tianyue Luo of ISCAS with the discovery. Ten models are affected, including the GS1900-8, GS1900-16, GS1900-24 and GS1900-48; each has a patched build ending in “.2)C0”, such as 2.90(AAHN.2)C0 for the GS1900-48.
What is not known: how many of the 996 devices have since been cleaned, whether the count has grown since GreyNoise's tally, and what the stolen credentials were used for next. CISA lists any ransomware link as unknown. Anyone running a GS1900 should check the firmware build, patch it, and rotate the switch's administrative credentials.
Sources
- CISA — Known Exploited Vulnerabilities CatalogPrimary source
- CISA Alert — CISA Adds One Known Exploited Vulnerability to CatalogPrimary source
- Zyxel Security Advisory — GS1900 seriesPrimary source
- NVD — CVE-2026-7273Primary source
- Help Net SecuritySecondary
- The Hacker NewsSecondary
Related
OpenAI Agent Breached Medicare Portal; Australia Told 84 Days Later
Attacks on WordPress RCE Flaw Rose Tenfold After Sept. 22 Fix
Arista VeloCloud Zero-Day at CVSS 10.0; Patch Due Sept. 25
Check Point: VPN Flaw Under Attack Since Sept. 12, Patch by Sept. 25
Malware Lets 4 AI Models Vote on Its Next Attack Move
Microsoft Shuts Down AI Phishing Service That Hit 12,000 Inboxes
F5 Patches Exploited BIG-IP Flaw; CISA Deadline Is Sept. 25
WordPress 7.1.1 Patches Click2Shell: One Link Installs a Theme
Trending now
- US-China Trade Truce Extended to Jan. 10 as Xi Visits
- Amoeba Breeds at 63°C, Past the 60°C Limit for Complex Life
- Oracle Invokes Force Majeure on 2.45GW Stargate Data Center
- Diller Drops $18B MGM Bid; Stock Falls 9.5% to February Levels
- Taylor Swift Adds 4 Songs to ‘Showgirl’ in Sept. 25 Encore
- Attacks on WordPress RCE Flaw Rose Tenfold After Sept. 22 Fix
- Rivian Recalls 98,828 EVs Over Rearview Camera Fault
- Arista VeloCloud Zero-Day at CVSS 10.0; Patch Due Sept. 25
Comments
No comments yet. Be the first.