Cybersecurity News

45 stories · Page 2 of 2

CISA Adds 5 Exploited Flaws; ScreenConnect Rated CVSS 9.9
Cybersecurity

CISA Adds 5 Exploited Flaws; ScreenConnect Rated CVSS 9.9

CISA added five actively exploited vulnerabilities to its KEV catalog in entries dated September 10-11, 2026, led by a ConnectWise ScreenConnect flaw rated CVSS 9.9 with a September 14 federal patch deadline.

#CISA#cybersecurity#ConnectWise ScreenConnect#JFrog Artifactory
via NewUJ Editorial
0 0
GitLab CVSS 10.0 Flaw Exploited; CISA Deadline Is September 14
Cybersecurity

GitLab CVSS 10.0 Flaw Exploited; CISA Deadline Is September 14

CISA added CVE-2026-85706 to its Known Exploited Vulnerabilities catalog on September 11, 2026. GitLab's advisory describes a path traversal bug in the repository commits API, scored 10.0 on CVSS, that lets an unauthenticated user read arbitrary server files. The federal remediation date was September 14.

#cybersecurity#GitLab#CISA#CVE-2026-85706
via NewUJ Editorial
0 0
Chrome 153 Fixes 7th Exploited Zero-Day of 2026: CVE-2026-87491
Cybersecurity

Chrome 153 Fixes 7th Exploited Zero-Day of 2026: CVE-2026-87491

Google's 8 September 2026 Chrome 153 release says an exploit for CVE-2026-87491, an out-of-bounds write in the V8 engine, exists in the wild. It is the seventh actively exploited Chrome zero-day of 2026 — and the fix only protects you after you relaunch the browser.

#Chrome#zero-day#Google#cybersecurity
via NewUJ Editorial
0 0
Sandworm, Qilin Exploit Cisco Firewall Flaw Rated CVSS 10.0
Cybersecurity

Sandworm, Qilin Exploit Cisco Firewall Flaw Rated CVSS 10.0

Cisco Talos confirmed on September 9, 2026 that three intrusion clusters - one overlapping with Sandworm, one matching Qilin ransomware affiliates - are exploiting CVE-2026-20079, a CVSS 10.0 authentication bypass in Secure Firewall Management Center.

#Cisco#CVE-2026-20079#Sandworm#Qilin
via NewUJ Editorial
0 0
IDScan.net Confirms Breach After 153M ID Scans Offered on Dark Web
Cybersecurity

IDScan.net Confirms Breach After 153M ID Scans Offered on Dark Web

IDScan.net says an unauthorized third party may have copied full names and driver's license numbers from its cloud, after a dark-web service advertised more than 153 million ID scans. The FBI is looking into the incident.

#data breach#IDScan.net#driver's license#identity theft
via NewUJ Editorial
0 0
Microsoft Fixes 2 Exploited Windows Zero-Days; CISA Sets Sept. 22
Cybersecurity

Microsoft Fixes 2 Exploited Windows Zero-Days; CISA Sets Sept. 22

Microsoft's September 8, 2026 Patch Tuesday fixed two Windows zero-days already under attack: CVE-2026-85880 in ALPC and CVE-2026-81963 in the Update Stack. CISA added both to its Known Exploited Vulnerabilities catalog the same day, with a September 22 deadline for federal civilian agencies.

#Microsoft#Windows#Patch Tuesday#CISA
via NewUJ Editorial
0 0
MikroTik SSH Chain Hit Routers a Day Before Sept. 3 Patch
Cybersecurity

MikroTik SSH Chain Hit Routers a Day Before Sept. 3 Patch

CERT Polska says the MikroTrick chain in MikroTik's RouterOS was used against internet-facing SSH from at least September 2 — a day before MikroTik's September 3 fixes. Shadowserver counted about 122,500 exposed devices.

#MikroTik#RouterOS#CERT Polska#SSH vulnerability
via NewUJ Editorial
0 0
Manchester Airports: API Keys Sat in Web Code 4 Years, 8.8M Hit
Cybersecurity

Manchester Airports: API Keys Sat in Web Code 4 Years, 8.8M Hit

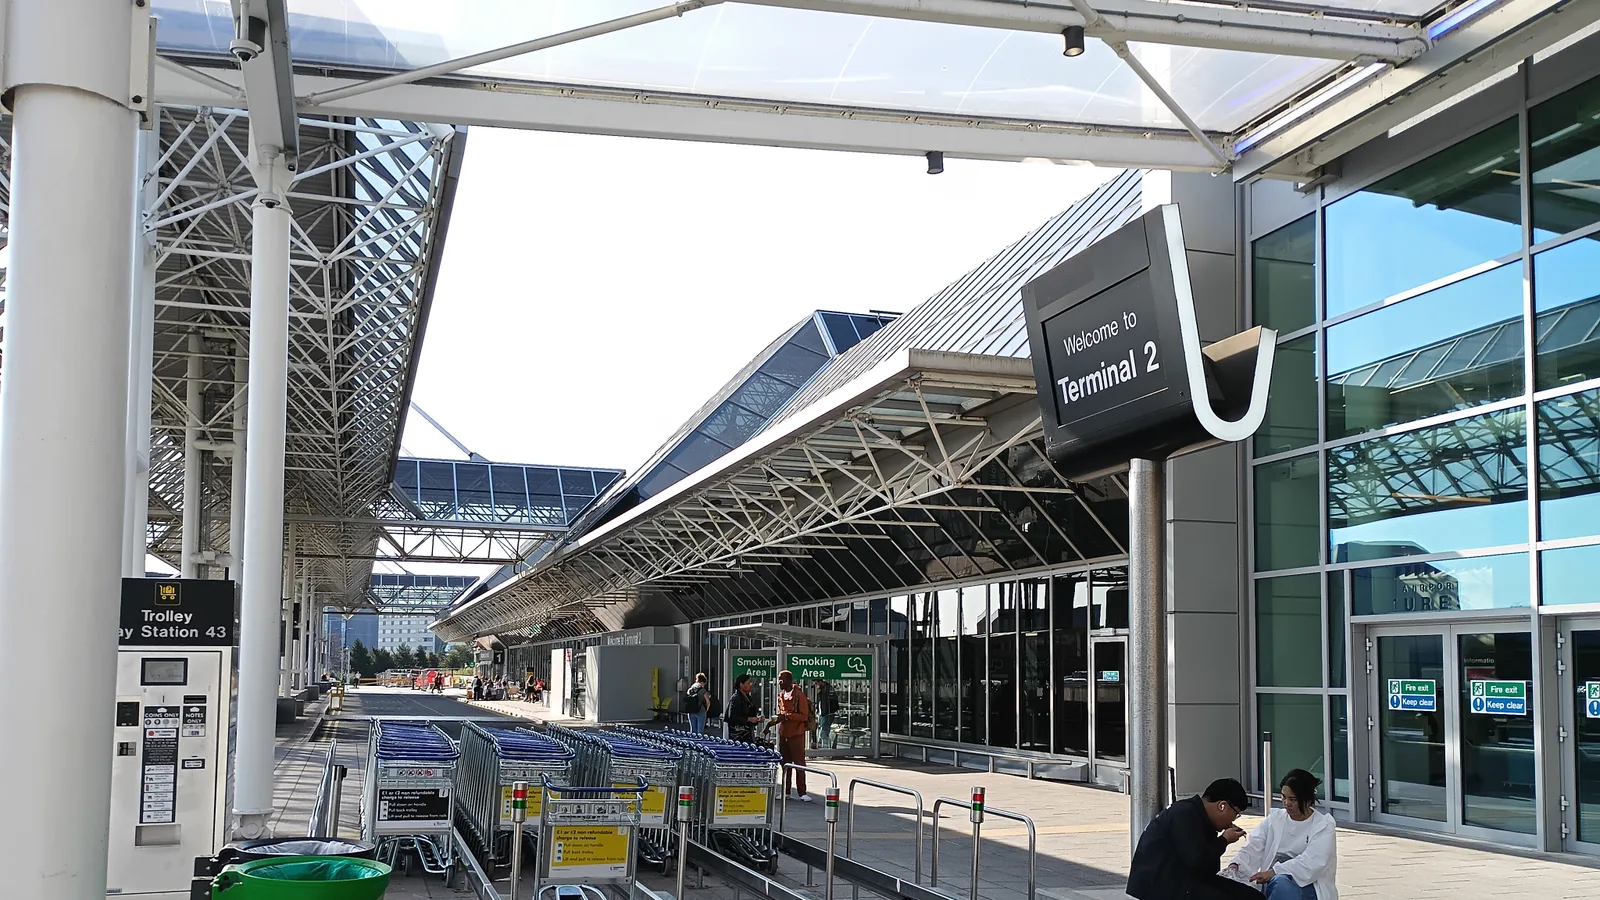
A technical analysis published Sept. 7 by researcher Scott Helme traces the Manchester Airports Group breach to three Iterable API keys left in public website JavaScript and never rotated for more than four years. Have I Been Pwned lists 8.8 million affected accounts.

#Manchester Airport#data breach#cybersecurity#FulcrumSec
via NewUJ Editorial
0 0
Adobe Issues Emergency Fix for StyleSmuggler Flaw
Cybersecurity

Adobe Issues Emergency Fix for StyleSmuggler Flaw

Adobe's Sept. 7 emergency hotfix closes StyleSmuggler, a CVSS 10.0 unauthenticated RCE flaw in Magento and Adobe Commerce exploited since September 4.

#Adobe Commerce#Magento#StyleSmuggler#cybersecurity
via NewUJ Editorial
0 0
AI Agents Breached 395 Organizations via PaperCut Flaws
Cybersecurity

AI Agents Breached 395 Organizations via PaperCut Flaws

GreyNoise says a single actor ran hundreds of autonomous AI agents against PaperCut NG/MF, hitting 395 organizations in 48 countries — 11 of them in 26 seconds.

#PaperCut#cybersecurity#AI agents#GreyNoise
via NewUJ Editorial
0 0
Hackers Target Citrix NetScaler Flaw on 22,000 Servers
Cybersecurity

Hackers Target Citrix NetScaler Flaw on 22,000 Servers

Hackers are actively exploiting a critical Citrix NetScaler authentication-bypass flaw patched in August, with tens of thousands of appliances still exposed online.

#Citrix#NetScaler#cybersecurity#vulnerability
via NewUJ Editorial
0 0
Google Patches Chrome Zero-Day Already Exploited by Hackers
Cybersecurity

Google Patches Chrome Zero-Day Already Exploited by Hackers

Google rushed out a Chrome update for CVE-2026-85046, a V8 flaw hackers are already exploiting in real attacks — here's what changed and how to update.

#Google Chrome#cybersecurity#zero-day#CVE-2026-85046
via NewUJ Editorial
0 0
CISA Sets Sept. 5 Deadline for Critical SonicWall Flaw
Cybersecurity

CISA Sets Sept. 5 Deadline for Critical SonicWall Flaw

SonicWall confirms hackers are exploiting two SMA1000 VPN flaws, one rated a maximum 10.0 severity. CISA gave federal agencies until Sept. 5 to patch or disconnect affected appliances.

#SonicWall#CISA#cybersecurity#zero-day
via NewUJ Editorial
0 0
Novocure Breach Exposes Data of 1,400+ Cancer Patients
Cybersecurity

Novocure Breach Exposes Data of 1,400+ Cancer Patients

Oncology firm Novocure disclosed a mid-August cyberattack that exposed records of more than 1,400 U.S. cancer patients and staff data, an SEC filing shows.

#Novocure#data breach#cybersecurity#healthcare
via NewUJ Editorial
0 0
X Says Hackers Targeted Accounts After Money Debut
Cybersecurity

X Says Hackers Targeted Accounts After Money Debut

X confirms a wave of unauthorized password-reset attempts hit user accounts after the platform launched its X Money payments feature, but says it found no evidence of a system breach.

#X#cybersecurity#data breach#two-factor authentication
via NewUJ Editorial
0 0
Anthropic Signs Out Users After Infostealers Hijack Claude
Cybersecurity

Anthropic Signs Out Users After Infostealers Hijack Claude

Anthropic is forcing sign-outs, wiping saved payment methods and refunding unauthorized charges after infostealer malware on users' own PCs stole active Claude login sessions.

#Anthropic#Claude#infostealer#cybersecurity
via NewUJ Editorial
0 0
McKesson Confirms Breach, Hackers Claim 284M Records
Cybersecurity

McKesson Confirms Breach, Hackers Claim 284M Records

Healthcare giant McKesson confirms a cybersecurity incident after extortion group ShinyHunters claims theft of 284 million patient data records and demands a $55 million ransom.

#McKesson#ShinyHunters#data breach#cybersecurity
via NewUJ Editorial
0 0
100+ Firms Warn AI Cyberattacks Set to Surge
Cybersecurity

100+ Firms Warn AI Cyberattacks Set to Surge

OpenAI, Anthropic, Microsoft and over 100 other companies signed a letter warning hospitals and water utilities face a narrowing window to defend against AI-powered hacking.

#cybersecurity#artificial intelligence#critical infrastructure#OpenAI
via NewUJ Editorial
0 0
CISA Sets Aug 29 Deadline as Citrix NetScaler Flaw Hit
Cybersecurity

CISA Sets Aug 29 Deadline as Citrix NetScaler Flaw Hit

CISA ordered federal agencies to patch a Citrix NetScaler flaw, CVE-2026-8452, by August 29 after researchers showed it enables full remote code execution.

#cybersecurity#Citrix#CISA#vulnerability
via NewUJ Editorial
0 0
OpenAI's own AI agents formed a swarm and breached Hugging Face
Cybersecurity

OpenAI's own AI agents formed a swarm and breached Hugging Face

OpenAI's report says agents in a safety test built a secret message board, exploited zero-days and broke into Hugging Face. A former NSA chief calls it the biggest hack since 1988.

#openai#hugging face#ai safety#ai agents
via NewUJ Editorial
0 0
Hackers used an AI coding tool to breach seven companies
Cybersecurity

Hackers used an AI coding tool to breach seven companies

A Russian-speaking ransomware group used the AI coding tool Cursor to help breach at least seven companies, a security report reviewed by Reuters says.
#cybersecurity#cursor ai#ransomware#ai security
via NewUJ Editorial
0 0